Secrets #
BuildPiper gives you a central and secure place to manage sensitive Kubernetes resources, called secrets. It connects directly with your Kubernetes clusters and fetches real-time secret data, so you can see everything from one platform. You can also create, configure and deploy secrets from the BuildPiper UI, with no manual terminal work.
1. Secret Management Overview #
| Capability | What it gives you |
|---|---|
| Centralised secure interface | Manage sensitive Kubernetes resources directly from BuildPiper, with real-time cluster visibility. |
| Real-time secret visibility | BuildPiper connects directly with the clusters and fetches real-time secret data. |
| Simplified operations | Create and deploy secrets without terminal-based Kubernetes work. |
| Dual-layer tracking | Track the secrets created in BuildPiper and detect the ones deployed directly to the cluster. |
| Flexible secret creation | You can create a secret in any of the following ways: • Key-value pairs, using the Guided Form or the Use Editor / Use YAML Editor option • Upload a secret manifest file • Provide a Git repository that contains the secret manifest file • Use a Helm template with a values file |
1.1 Dual-Layer Secret Tracking #
BuildPiper manages the full lifecycle of the secrets it creates. It also detects the secrets that were deployed directly to the cluster. This gives you an accurate view of the cluster and helps you find unmanaged or “shadow” credentials before they become a security risk.
| Type | What it means |
|---|---|
| BuildPiper-created secrets | Secrets created from the BuildPiper UI. The platform manages their lifecycle. |
| External secrets | Secrets deployed directly to the cluster. BuildPiper detects them for governance and security visibility. |
2. Configuration #
2.1 Open Secrets and Add a Secret #
The Secrets page is available only in the User Portal.
- 1
Log in to BuildPiper.
- 2
Click Application.
- 3
Click Environment Overview.
- 4
Select the environment.
- 5
Click the Secrets tab.
- 6
Click Add Secret to create a new secret. See section 2.4 for the form.
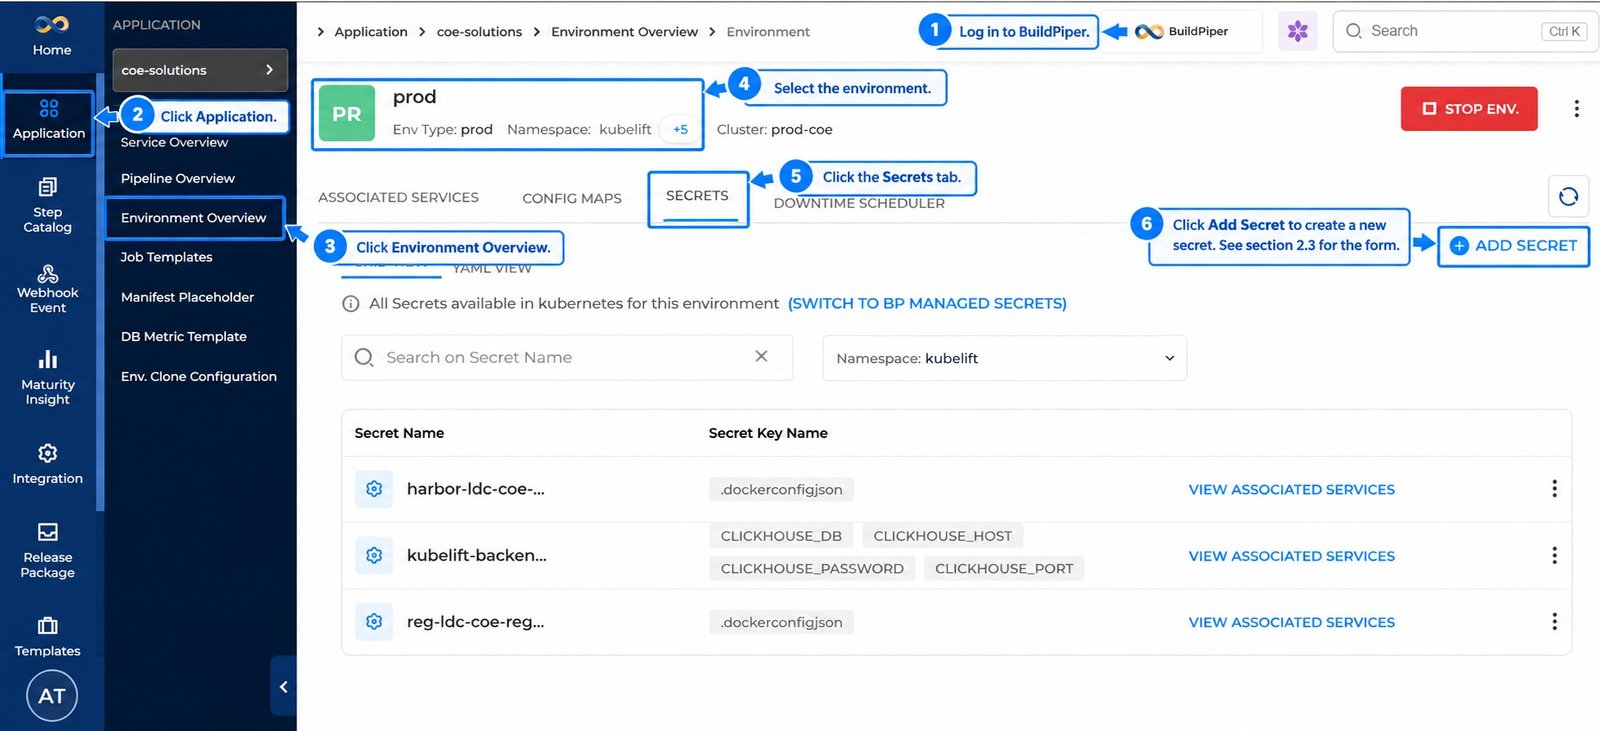
Figure 1: Steps to open the Secrets tab
The page has these parts:
| Item | What it does |
|---|---|
| Environment header | Shows the environment name, type, namespace and cluster, with the Stop Env. button and a 3-dot menu. A +5 next to the namespace means more namespaces are mapped to the environment. |
| Grid View / YAML View | Shows the list as a grid, or as YAML. |
| Add Secret | Opens the form to create a new secret. |
| Switch to BP Managed Secrets | Switches the list to the secrets managed by BuildPiper. The list otherwise shows all the secrets available in Kubernetes for the environment. |
| Search on Secret Name | Finds a secret by name. |
| Namespace filter | When multiple namespaces are assigned to an environment, select a namespace from the dropdown menu to view the secrets of that namespace. |
| List | Shows each secret name and its key names. View Associated Services shows the services that use it, and the 3-dot menu shows more actions. |
2.2 Grid View and YAML View #
Use the two links under the tabs to change how the secrets are shown.
| View | What it shows |
|---|---|
| Grid View | The secrets as a list, with the name and key names of each one. See Figure 1. |
| YAML View | The YAML of the secrets in the environment, in a code editor with line numbers. It starts with apiVersion and items, and each item has its data, metadata (such as the creation time, name, namespace and uid) and type. See Figure 2. |
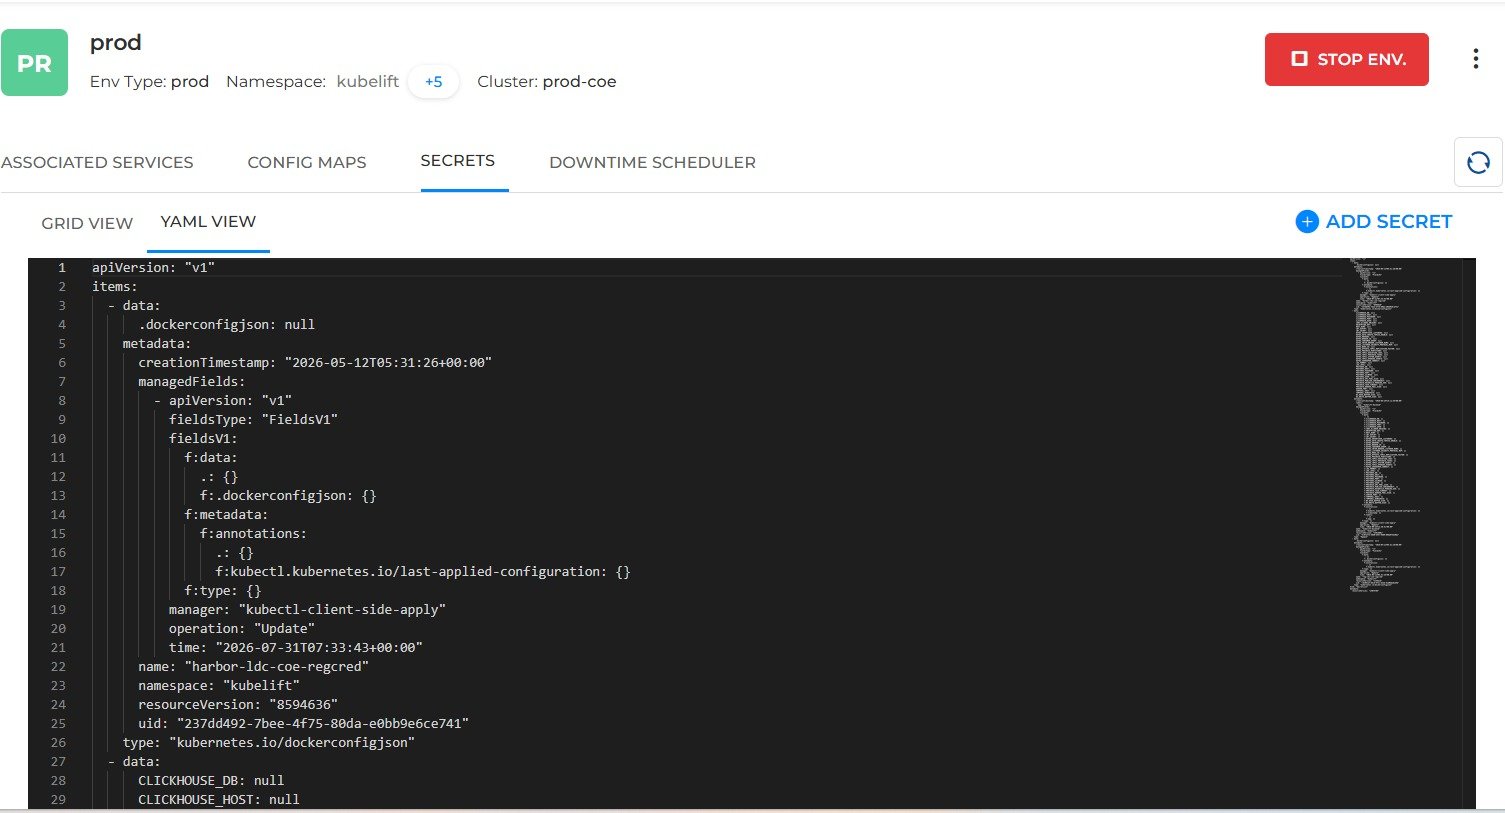
Figure 2: YAML View of the secrets
2.3 Input Methods #
Select the method with the radio buttons in the form. Fields marked * are required.
Note: If multiple namespaces are configured in the environment, the Select Namespace drop-down lists all of them. Select one namespace from the list. This applies to all the input methods below.
| Input method | Use it to |
|---|---|
| Guided Form | Enter the data as key-value pairs. |
| Upload Custom Manifest file / GitOps | Upload a YAML manifest, import one from a Git repository, or use a Git-based Helm template and values file. |
| Use Editor | Paste key-value pairs in a text area. |
| Use YAML Editor | Paste the full YAML. |
Guided Form #
| Field | What to do |
|---|---|
| Key* | Enter the key name. |
| Provide a value / File Upload / File via Git | Select how to give the value of the key. Provide a value lets you type it. File Upload and File via Git take the value from a file. |
| Add value* | Enter the value. It is hidden by default. Click the eye icon to show it. |
| Add Row | Adds another key-value pair. |
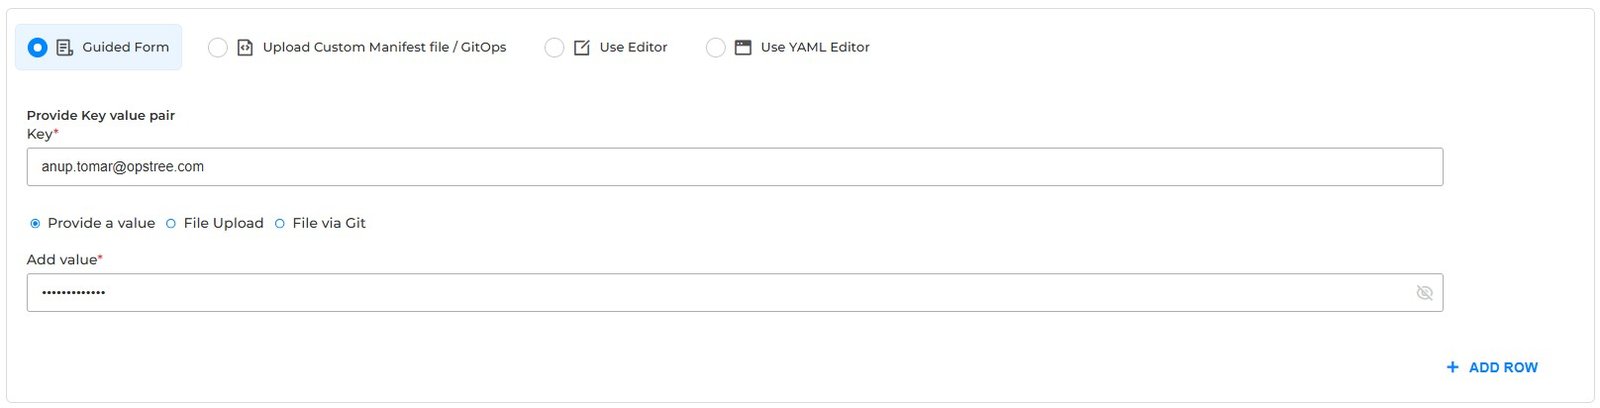
Figure 3: Guided Form
Upload Custom Manifest file / GitOps #
Select one of three ways to give the manifest.
| Option | What to do |
|---|---|
| Via Manifest File Upload | Drag and drop the file, or click click here to choose it. You can upload more than one file. Make sure the Secret Name is the same as the name in the manifest file and that the file has valid key-value pairs. |
| Via Git URL | Get the manifest from a Git repository. See the steps below. |
| Via Helm Templates | Create the secret from a Helm template. See the steps below. |
Via Git URL #
Make sure the Secret Name is the same as the name in the manifest file.
- 1
In Please Select the Git URL*, select the repository from the drop-down.
- 2
Click Load Branches to get the branches of the repository.
- 3
In Select Branch*, select the branch, for example dev-test.
- 4
In File or folder Paths, enter the path of the file or folder that has the secret key-value pairs, for example abc.yaml or xyz-folder. Click Add Row to add more paths. Use the delete (bin) icon to remove a path.
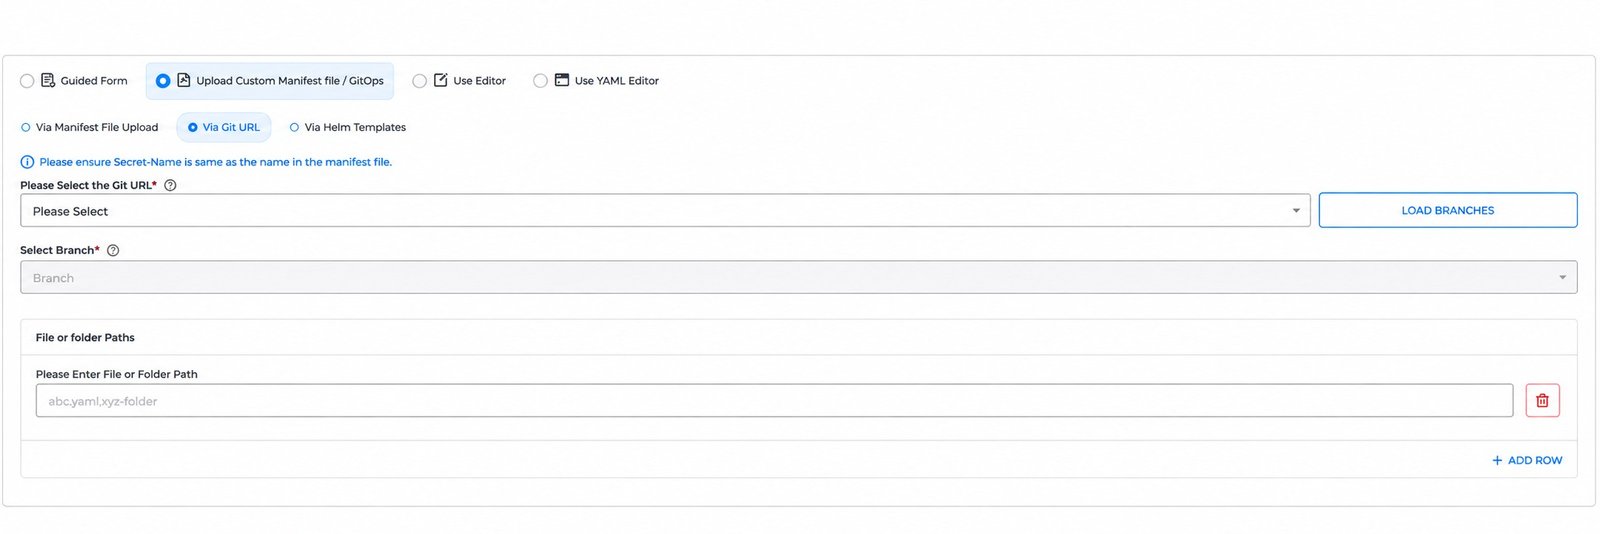
Figure 4: Upload Custom Manifest file / GitOps, Via Git URL
Via Helm Templates #
Make sure the Secret Name is the same as the name in the manifest file. Under Helm Templates, select Git Repo or Helm Repo. The steps below are for Git Repo.
- 1
In Please Select the Git URL*, select the repository from the drop-down. Click Load Branches.
- 2
In Select Branch*, select the branch.
- 3
In Please Enter File or Folder Path*, enter the path of the Helm template, for example k8s/abc.yaml.
- 4
Enter a name in Helm Release Name.
- 5
Under Value Files, select Via File Upload or Via Git Repo. For Via File Upload, drag and drop the file, or click Choose file, in Please upload the file*.
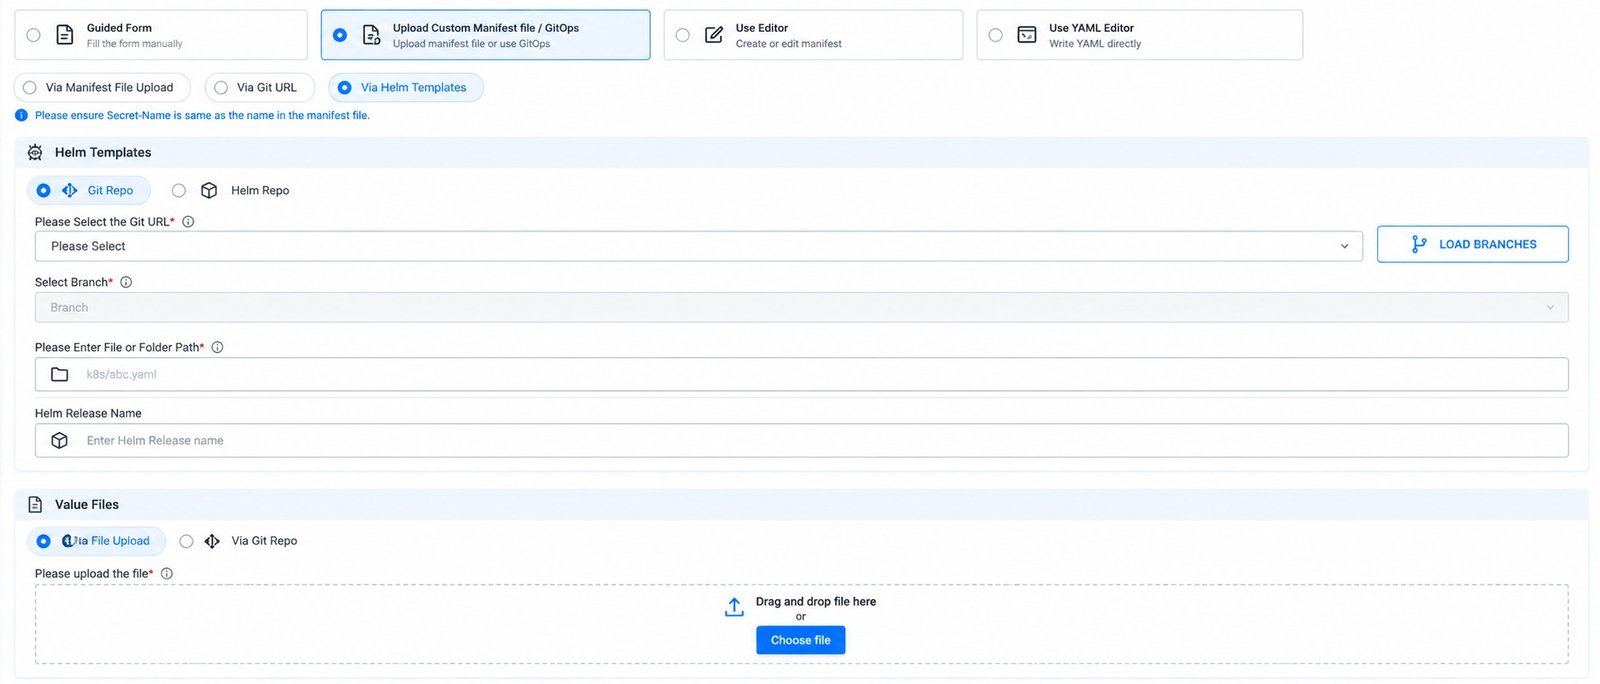
Figure 5: Upload Custom Manifest file / GitOps, Via Helm Templates
Use Editor and Use YAML Editor #
| Input method | What to do |
|---|---|
| Use Editor | Paste key-value pairs only, one per line, in the form key=value. |
| Use YAML Editor | Paste YAML content only, for example key: value. |
2.4 Add Secret Form #
- 1
On the Secrets tab, click Add Secret. The Add Key/Value Secrets form opens.
- 2
Fill in the fields in the table below.
- 3
Click Save to save the secret, or click Save & Deploy to save and deploy it in one step.
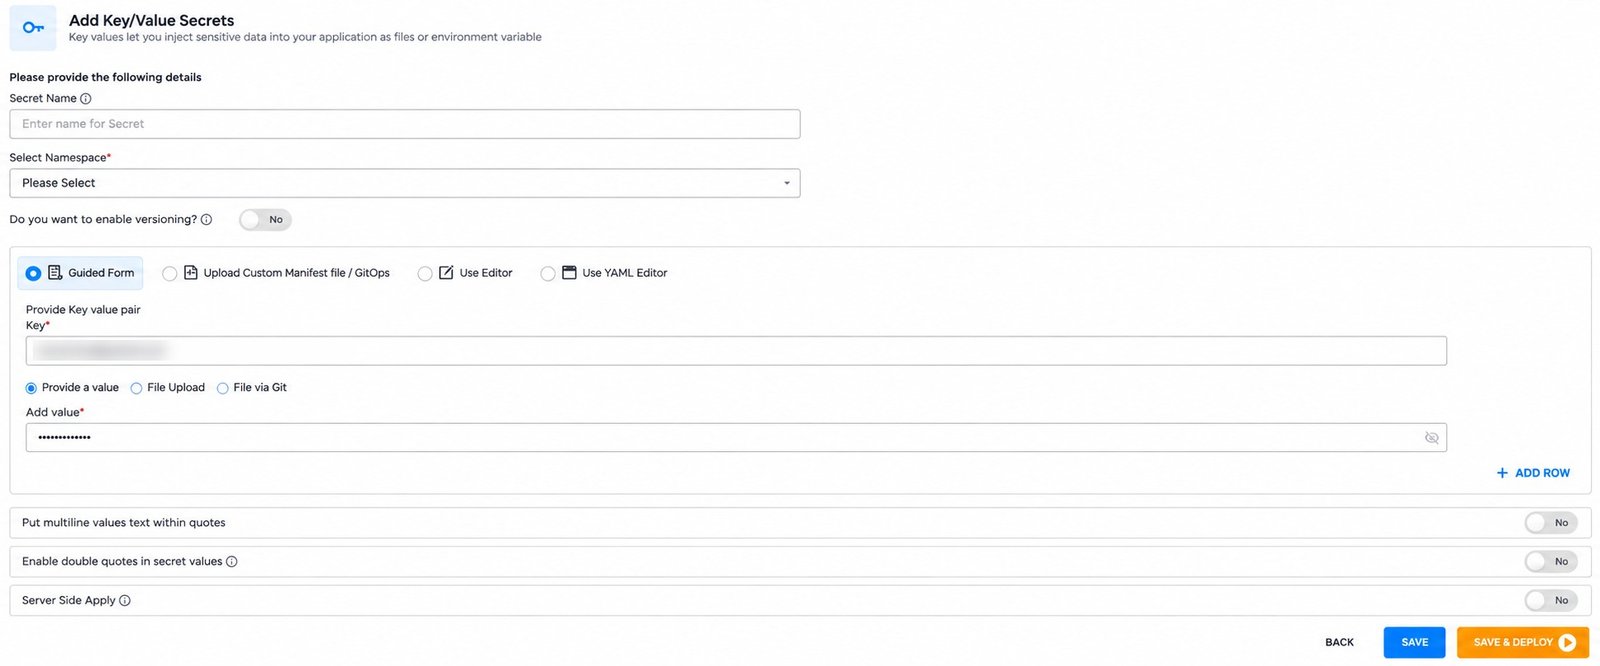
Figure 6: Add Key/Value Secrets form (Guided Form)
| Field | Required | What to do |
|---|---|---|
| Secret Name | Yes | Give the secret a unique name. You use this name later as the secret name in the deployment settings. |
| Select Namespace | Yes | When multiple namespaces are assigned to an environment, you can select a namespace from the dropdown menu to view the Secrets associated with that namespace. |
| Do you want to enable approval? | No | Enable this option to require approval before the ConfigMap changes are applied. When it is enabled, the changes must be approved according to the configured approval workflow before they proceed. The default is Disable |
| Input method | Yes | Choose how to give the data: Guided Form, Upload Custom Manifest file / GitOps, Use Editor or Use YAML Editor. See section 2.3. |
| Put multiline values text within quotes | No | When on, BuildPiper automatically wraps data that spans several lines in quotes, so the format stays correct. The default is No. |
| Enable double quotes in secret values | No | Kubernetes requires values to be enclosed in double quotes. Enable this setting to have BuildPiper automatically wrap every ConfigMap value in double quotes if the values are not already quoted. The default is Disable. |
| Server Side Apply | No | An advanced Kubernetes feature. The cluster server manages the merges and updates of the configuration, instead of the local client. The default is No. |
| Button | What it does |
|---|---|
| Save | Saves the secret. |
| Save & Deploy | Saves the secret and deploys it. |
3. Actions #
These are the actions you can take on a secret from the Secrets tab.
3.1 View Associated Services [coming soon] #
In the BP managed list you can see which services use each secret.
- 1
On the Secrets tab, click Switch to BP Managed Secrets. To go back to the full list, click Switch to All Secrets Available.
- 2
On the secret row, click View Associated Services.
- 3
A panel opens under the row and lists the services that use the secret.
- 4
Click the X to close the panel.
Screenshot needed: Figure 6: the panel that opens after View Associated Services on a secret
3.2 3-dot Menu Actions #
Click the 3-dot menu at the end of a secret row to see the actions.
| Action | What it does |
|---|---|
| Edit | Opens the secret so you can change it. |
| Delete | Deletes the secret. |
| Re-deploy | Deploys the secret again. |
| View Yaml | Shows the YAML of the secret. |